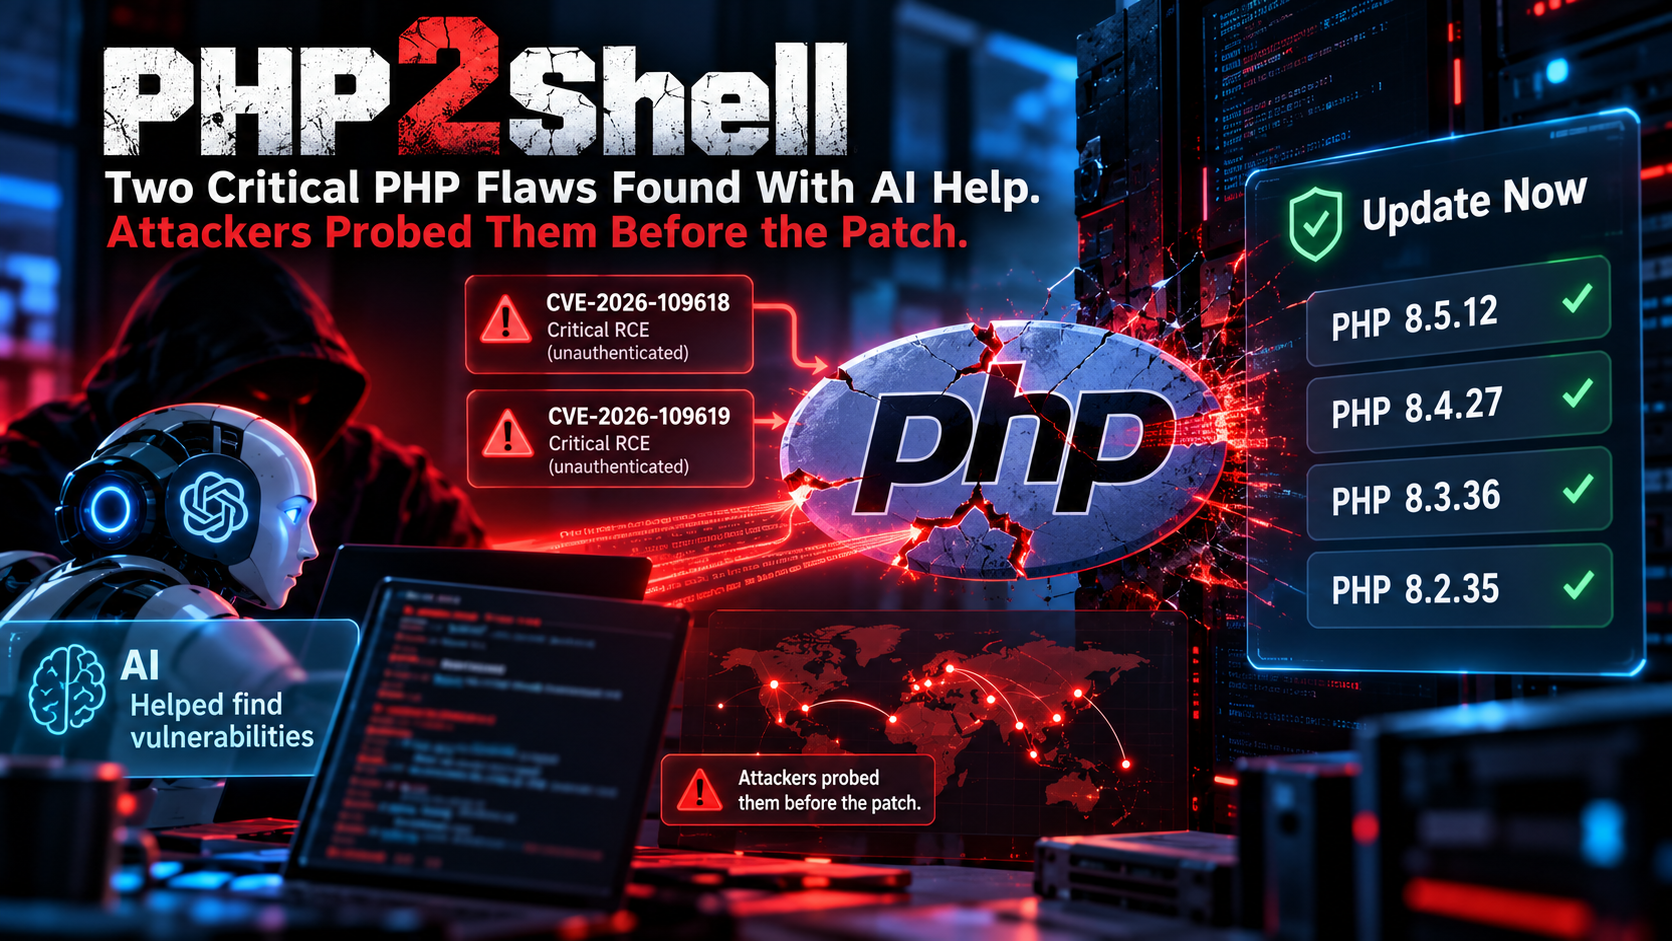
PHP shipped emergency security patches on Wednesday, October 21, for two critical flaws known as PHP2Shell. They are CVE-2026-109618 and CVE-2026-109619, and both could let an attacker run code on a web server remotely without logging in. The fixes are in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Both are rated 9.2 on the CVSS v4.0 scale, which tops out at 10. What to do now. The flaws affect PHP installations that serve web requests, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed. The fix is to update. For CVE-2026-109618, PHP’s interim guidance was to set memory_limit=-1, ideally in a way applications can’t override, and for CVE-2026-109619 on PHP 8.5 to set fatal_error_backtraces=0 and restart every worker. The advisory warns the memory-limit step is not complete protection. Follow PHP’s official advisories for the authoritative steps. What the flaws are. CVE-2026-109618 involves PHP’s out-of-memory handling, which can interrupt a request while internal data is only partly set up. CVE-2026-109619 involves request-owned state that survives after its memory has been freed. The PHP Foundation said CVE identifiers that circulated before the release came with an incorrect score of 10.0. Treat it as urgent, because attacks started early. Amazon Threat Intelligence said its honeypot network recorded a PHP2Shell exploitation attempt on October 17, four days before public disclosure. Cloudflare’s CTO said the company was already seeing early attacks, and had deployed firewall rules aimed at known exploitation methods. Cybersecurity News also reported a public testing tool and early exploitation attempts. The PHP Foundation moved the release up by a day after the CVE identifiers leaked. The AI angle, and a dispute over credit. The flaws surfaced during a source-code audit that OpenAI funded through its Patch the Planet initiative, and Google’s Wiz team says it found them independently, weeks later, using Wiz Atlas, Gemini 4 Argon and GPT-5.6 Sol. PHP’s advisory credits researchers from Calif, Wiz and OpenAI together. OpenAI said Calif identified a critical flaw using GPT-5.6 Sol, but Calif later credited an independent researcher, @lcfr_hax, with first finding PHP2Shell and building a working exploit. The sources agree AI tools played a role, but they differ on who found what first, and none shows how much of the work the AI did unaided. A double-edged result. OpenAI said it expects similar findings to increase sharply in the coming months. Wiz researchers said frontier AI models substantially lowered the barrier to turning a longstanding flaw into an exploit. The same capability that helped defenders find the bugs can help attackers, which is the point both companies make. About the “70% of websites” figure. Wiz estimates that PHP runs roughly 70% of all websites. That’s an estimate of how widely PHP is used, not a count of vulnerable or exposed sites. Nothing in the public disclosures quantifies how many deployments were actually at risk, so the figure shows PHP’s reach, not the size of the exposure. Bottom line: For anyone running PHP on a web server, the action is plain: update to a fixed version now, since exploitation attempts began before the patch existed. For everyone else, PHP2Shell is a concrete case of AI-assisted vulnerability research finding a serious, long-standing flaw, with open questions about credit and about how much of the work the tools actually did. It also shows the dual-use problem that security teams have been warning about, in a case where attackers were probing before defenders could patch.
OpenAI
PHP2Shell: Two Critical PHP Flaws Found With AI Help. Attackers Probed Them Before the Patch.
PHP shipped emergency patches for PHP2Shell, two critical unauthenticated remote code execution flaws (CVE-2026-109618, CVE-2026-109619). Update to 8.5.12, 8.4.27, 8.3.36 or 8.2.35.
10 views3 min readKainotomic Team
Key takeaways
- PHP shipped emergency security patches on Wednesday, October 21, for two critical flaws known as PHP2Shell.
- They are CVE 2026 109618 and CVE 2026 109619, and both could let an attacker run code on a web server remotely without logging in.
- Both are rated 9.2 on the CVSS v4.0 scale, which tops out at 10.