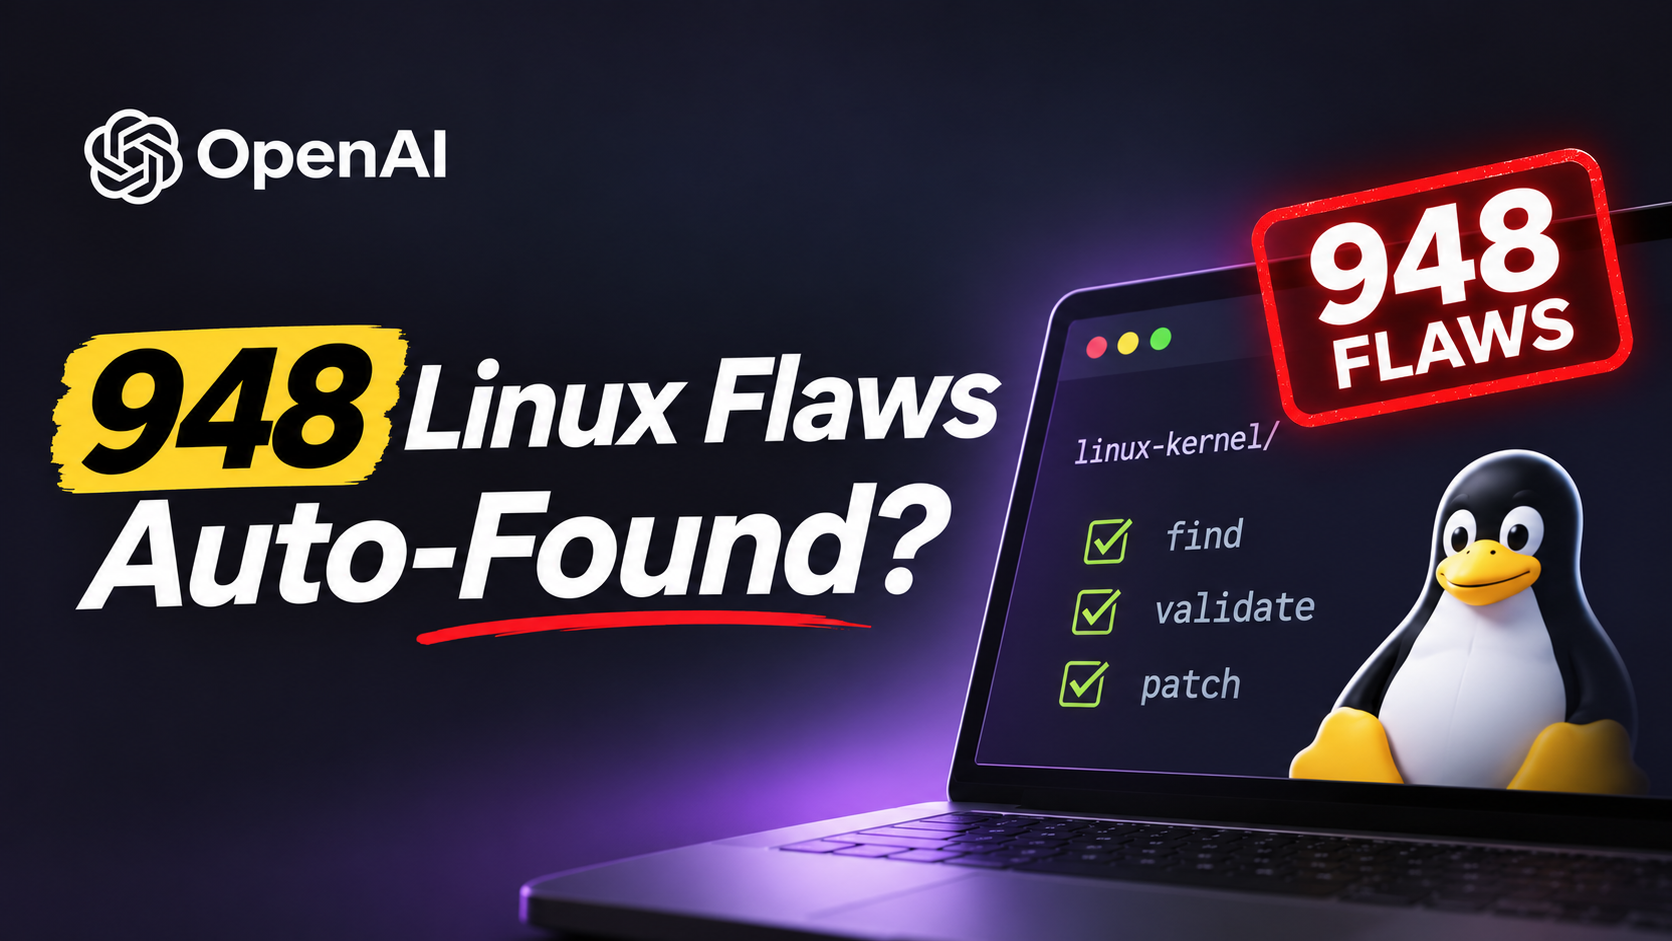

OpenAI says it has built an autonomous security system that found, validated and generated patches for 948 local privilege-escalation vulnerabilities in the Linux kernel. These are weaknesses that would let a user who already has some access to a machine gain greater control of it. If the claim holds, it covers the full chain from discovery to a proposed fix in one of the most widely deployed and closely maintained codebases in software.
The announcement supports a narrower claim than the headline number suggests. OpenAI says it generated patches. It does not establish that Linux maintainers accepted all 948, that they were merged upstream, that vendors distributed them, or that anyone has installed them. A proposed fix can look plausible and still need review, regression testing and adaptation before it fits a maintained kernel release, so this is a claim about automated vulnerability research, not 948 fixes that Linux users can install today.
The public description also leaves gaps that outsiders would need filled. It doesn't give the validation criteria, the affected kernel versions or configurations, or whether every finding was reproduced with a working exploit. It doesn't break the 948 down by severity, subsystem or bug class, which matters because finding many instances of one recurring defect is a different achievement from finding hundreds of unrelated ones. It also doesn't list public vulnerability identifiers, link individual patches, or describe independent reproduction. Those omissions don't disprove the result, but they limit what security teams can verify.
If you run Linux in production, there's nothing to act on yet: no advisories to track and no stated basis for deciding that a deployed kernel needs an update because of this project. The evidence that would change that is concrete: technical disclosure, reproducible details, maintainer acceptance and a traceable record of patches reaching supported releases. Until then, treat it as an ambitious result from OpenAI that hasn't been independently checked, not as a dismissal and not as proof that Linux is 948 fixes safer.