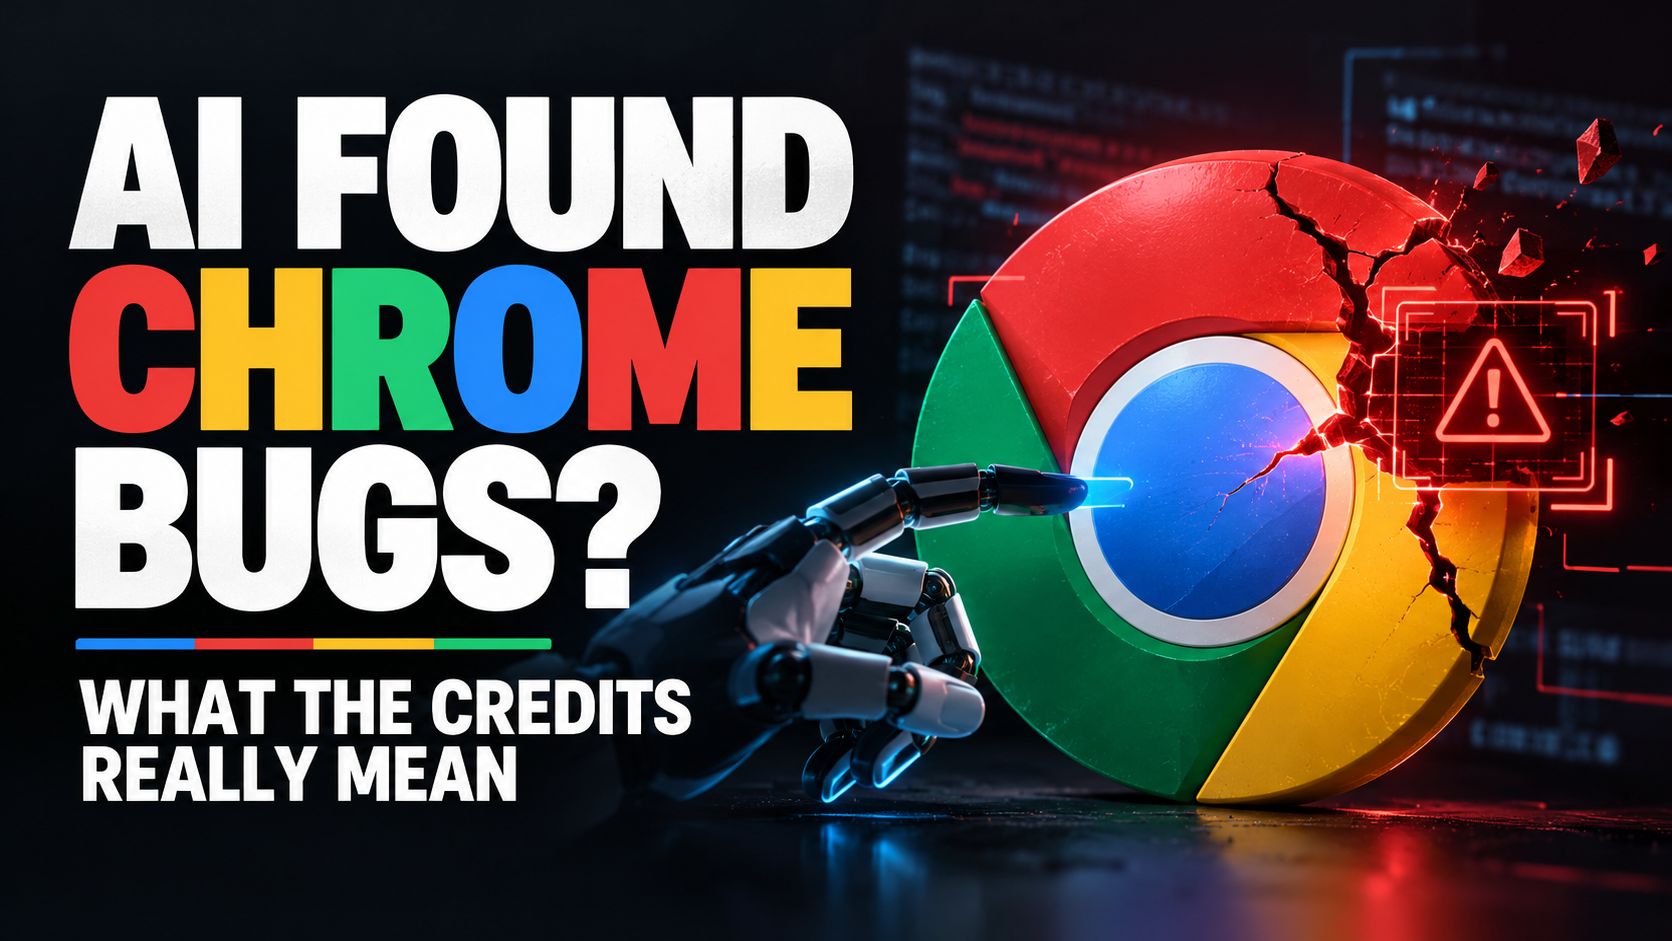

Google released Chrome 156.0.8078.73/.74 for Windows and Mac and 156.0.8078.73 for Linux, fixing 52 security issues. The update includes four rated Critical. According to Google’s October 27 stable-channel note, four of the High-severity issues are use-after-free bugs credited to OpenAI Codex Security, in the components Google lists as Turbolev, ImageCapture, Video, and PDFium. PiunikaWeb describes them as memory bugs in the PDF viewer, video handler, and JavaScript engine.
What a use-after-free is. It happens when software keeps using a piece of memory after it has been released. Depending on the code, that can cause a crash or, in some cases, let an attacker run code. Google’s note classifies all four as High severity but doesn’t describe how any of them could be exploited, and this article doesn’t either.
This isn’t the first Codex Security credit in Chrome 156. The initial Chrome 156 stable release on October 20 fixed 353 vulnerabilities, six of them Critical. Reporting on that release says an OpenAI Codex Security researcher, “kylebot,” was credited with a critical memory-corruption bug in WebRTC. To keep the picture balanced, the same release credits Xinyang Ge of Anthropic, with assistance from Claude, for a critical use-after-free in Accessibility. Mozilla also credits Codex Security for bugs fixed in a recent Firefox release.
What the credits don’t show. A credit means Chrome’s security process accepted the reports. It doesn’t say how the bugs were found, whether an automated system found them without human direction, how much researcher review was involved, or whether the approach would work reliably at scale. None of the sources report that these four bugs were exploited in the wild.
What to do. Open About Google Chrome from the settings or Help menu, let it check for updates, and click Relaunch. A download prompt alone isn’t enough, since the old browser process can keep running until you relaunch. IT teams managing Chrome deployments should treat this as a security update to roll out promptly. Google traditionally holds back some vulnerability details until most users have updated, so more may be published later.
Bottom line: For users, the takeaway is to update and relaunch. For anyone following AI and security, the credits are one more data point that AI-assisted tools are appearing in browser bug reports, from both OpenAI and Anthropic. They show accepted reports, not an autonomous breakthrough, and the sources don’t say how much of each discovery was the tool’s work.