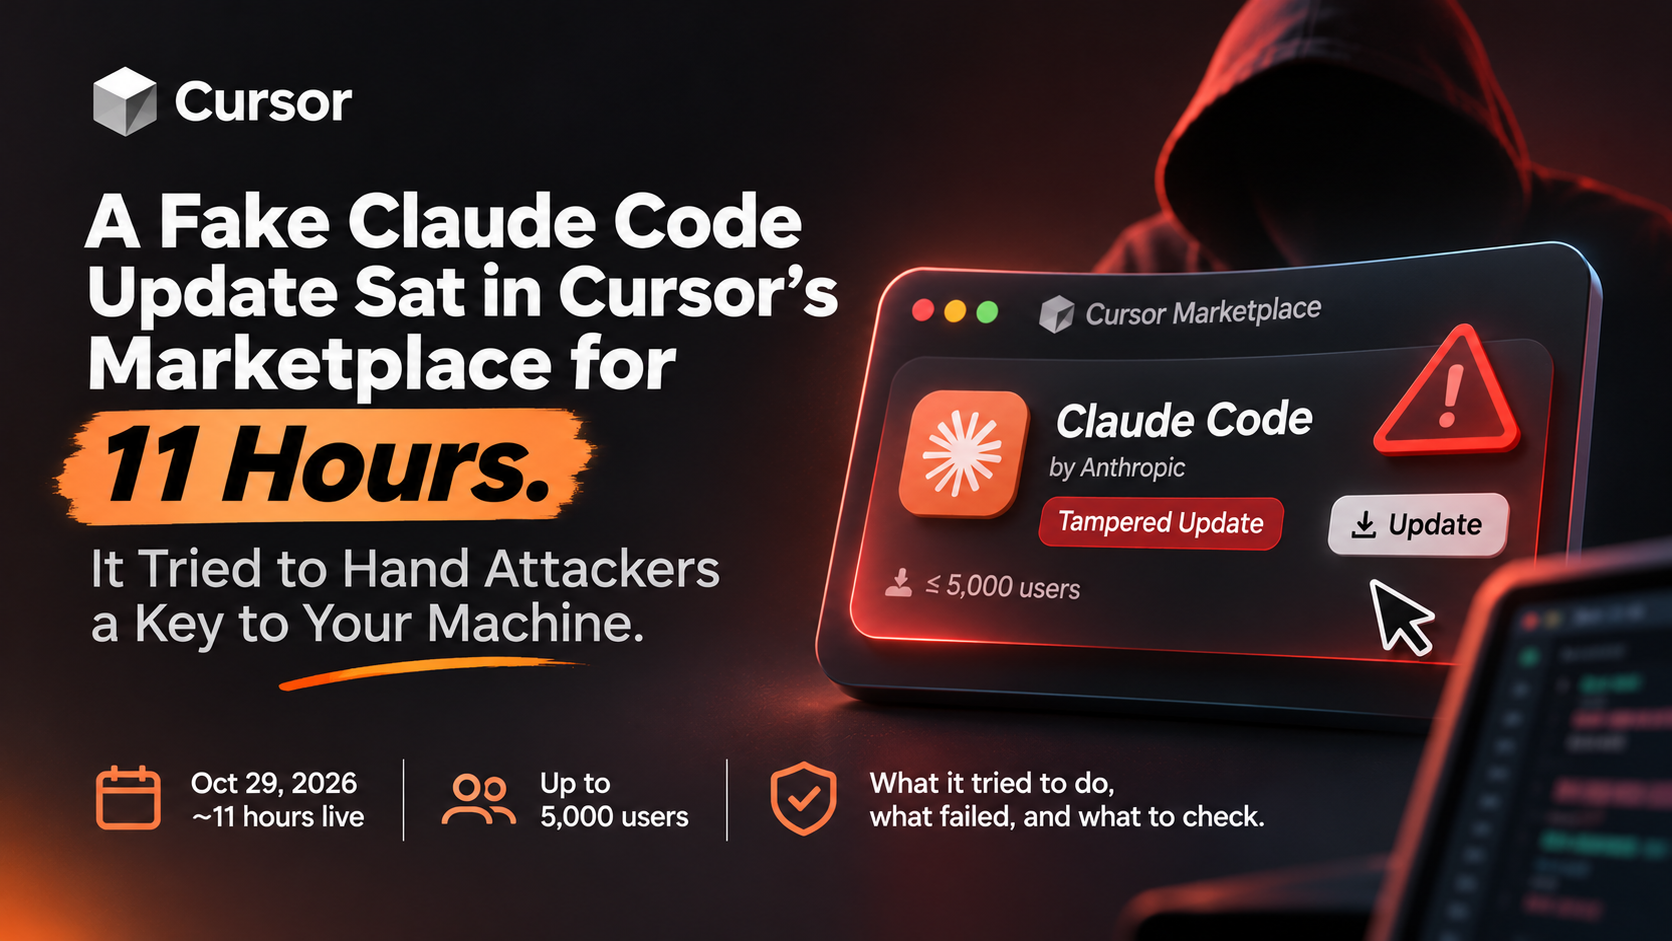

Cursor has pulled two tampered releases of a Claude Code-branded extension after they tried to plant a persistent SSH backdoor on developer machines. The versions, 2.1.312 and 2.1.313, were available in Cursor’s marketplace from about 2:27am to 1:35pm PT on October 29, and Cursor says Anthropic did not build them. This wasn’t a routine buggy-extension story. Cursor shut the marketplace down, audited access, rotated its keys and rebuilt it before bringing it back. Companies don’t do that for a bad release. They do it when the distribution channel itself looks compromised.
Microsoft’s analysis gives the clearest picture of what the code was built to do. An injected loader ran as soon as the extension loaded, ahead of the real code. It tried to add an attacker’s SSH key, switch on the local SSH service, open a reverse tunnel and set up persistence, then report host details back. If every step worked, that combination would let an attacker reconnect to a developer’s machine long after the install. Developer machines tend to hold source code, cloud credentials and access to internal systems, which is why a hostile extension there is worse than a hostile browser tab.
The harder question is how many people were actually hit, and nobody has answered it. Cursor has said at most 5,000 users were affected, but that’s a ceiling. As far as I can find, there’s no public count of actual installs, successful backdoors, attacker logins or stolen data. Microsoft says the loader collected the names of environment variables that looked sensitive, not their values. That doesn’t prove nothing was taken, but it isn’t proof of theft either.
There’s real good news in the detail. Cursor says switching on SSH needs admin rights the extension lacks on most Macs and Windows machines, so the attacker likely couldn’t log in on those. It also says it worked with the hosting provider to take the attacker’s server offline. The cleanup warning matters just as much. The payload left scripts outside the extension’s folder, so uninstalling it may not be enough. Anyone who ran the affected versions on Mac or Windows that day should use the check and removal scripts in Cursor’s notice, then rotate any credentials the machine could reach.
The blast radius is also narrower than the “Claude Code” name suggests. Microsoft says the malicious packages were never published to the Visual Studio Marketplace or to npm, and that Anthropic told it its systems weren’t compromised. Anthropic’s Felix Rieseberg said on X that someone used access to Cursor’s marketplace to publish the modified extension. That makes this a Cursor marketplace incident, not a break-in at Anthropic. What nobody has explained publicly is how the attacker got that access in the first place.
The lesson is uncomfortable. AI coding tools inherit the security of wherever they’re downloaded from, and a trusted name on a trusted marketplace looked like a routine update. Microsoft points organizations to Cursor’s hardening options, including approved-publisher lists and a cooldown that delays installing newly published versions. Until the how is explained, those controls are the practical defense.